

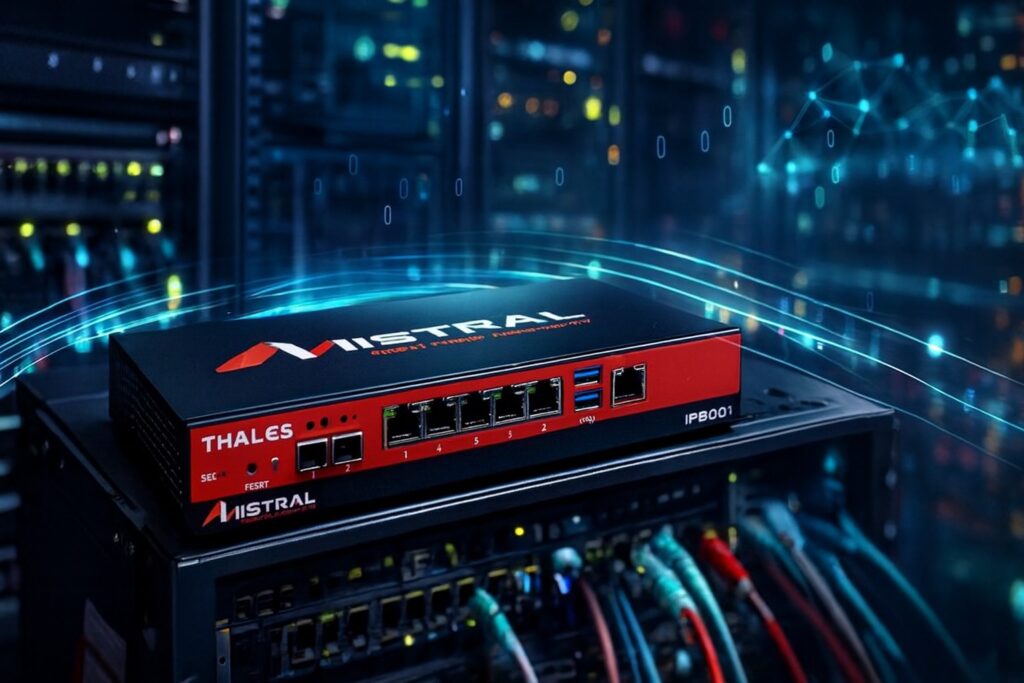
Thales Unveils Mistral: A Post-Quantum Encryptor for Sensitive European Communications
At the European Cyber Week in Rennes, Thales introduced Mistral, a cutting-edge post-quantum encryptor designed specifically for securing sensitive communications across Europe. This significant advancement is set to strengthen the security frameworks of public administrations, critical operators, and defense industries in preparation for a post-quantum world. Mistral meets the stringent requirements set forth by the French National Cybersecurity Agency (ANSSI) and builds on a lineage already certified by NATO. It combines high-level encryption, impressive performance, and centralized management capabilities.
The timing of this launch comes as organizations dealing with classified or sensitive information strive to fortify their infrastructures against potential quantum attacks. Thales aims to evolve its Mistral family, which has been deployed for years by various ministries, strategic operators, and NATO entities, into a robust encryptor now fortified against advanced cryptanalysis. The company emphasizes that this technological leap is essential for future European projects that demand protection at the Restricted Dissemination level, a category where regulatory requirements are rapidly intensifying.
The new post-quantum Mistral retains the proven capabilities of the TRC7535 and TRC7539 generations while integrating algorithms resilient against quantum attacks. Certified to Common Criteria EAL4+ standards per ANSSI recommendations, the device ensures the confidentiality and integrity of IP flows through dedicated hardware processing, finely-tuned encryption policy selection, and strict separation between clear and encrypted traffic. With announced performance capabilities reaching a cumulative 4 x 10 Gbit/s while maintaining low latency, Mistral is tailored for industrial networks and critical interconnections where every millisecond counts.
An Architecture Tailored for Upcoming European Standards
Thales leverages the modular architecture of its Mistral units, centered around encryption capabilities, the Mistral Management Center (CGM), and the Key Generation Center (CEC). This structure facilitates the isolation of data streams, management of thousands of tunnels, and adherence to organizational security policies. The CGM enables centralized and redundant administration, capable of remotely configuring devices across isolated networks. By building on this foundation, Thales introduces post-quantum capabilities while ensuring a seamless transition for existing infrastructures.
The equipment is distinguished by its internal control mechanisms, inherited from NATO-certified versions: cryptographic self-tests, emergency power-off erasure, symmetric key management with controlled crypto periods, and alerting the CGM in cases of network anomalies or configuration drift. Network topology and security policies remain protected against eavesdropping or modification attempts thanks to ESP tunnels compliant with national hardening practices. This continuity ensures quick integration into cross-border projects where common compliance is a prerequisite.
A Response to Quantum Threats and Sovereignty Needs
By anticipating the emergence of post-quantum computing capabilities, Thales presents a solution designed to sustainably protect sensitive communications. The company notes that Europe’s heavy reliance on classical IP encryptors poses risks of retrospectively deciphering data if currently intercepted information is stored pending quantum advancements. Industrial availability is projected for June 2026, enabling public sectors and key industrial players to begin modernizing their equipment as early as 2025, aligning their security policies with European roadmaps for hybrid encryption.
According to Pierre Jeanne, Vice President of Sovereign Cybersecurity Solutions, the goal is to provide France and its partners with an encryptor “capable of withstanding quantum attacks,” while maintaining the performance levels expected by operational networks. Vital operators, state agencies, and high-tech industries will have access to equipment ready to protect classified exchanges at the restricted level, especially as European administrations bolster their requirements for the cryptographic resilience of network equipment, particularly for joint defense programs.
Integration Designed for Critical Environments
Mistral is currently undergoing operational testing with several partners, adhering to evaluation practices outlined in previous technical documents. Tests specifically examine compatibility with existing infrastructures, the robustness of IP tunnels under load, resistance to network attacks, and the integrity of remote management functionalities. The targeted mid-2026 availability allows organizations ample time to plan a structured migration, incorporating key management requirements, filtering policies, and Mistral’s multi-point authentication mechanisms.
This approach is particularly relevant for ecosystems handling sovereign data, such as the space industry, defense, energy operators, and ministries working within segmented architectures. Interoperability with previous generations allows modernization of the most sensitive segments without necessitating a complete network reconfiguration. In the context of European initiatives aimed at secure next-generation communications, Mistral positions itself as a convergence point for operational demands, regulatory constraints, and preparation for a post-quantum future.



