

Washington to Involve Private Industry in Cyber Offensive Strategy
Washington is reportedly crafting a national cybersecurity strategy that would explicitly enlist private companies in offensive cyber operations. According to revelations from Bloomberg, the forthcoming plan aims to formalize the participation of industry players in disruptive, neutralizing, or retaliatory actions against states and criminal organizations. This shift is not an isolated incident; rather, it represents a culmination of recent initiatives and publications from the U.S. government.
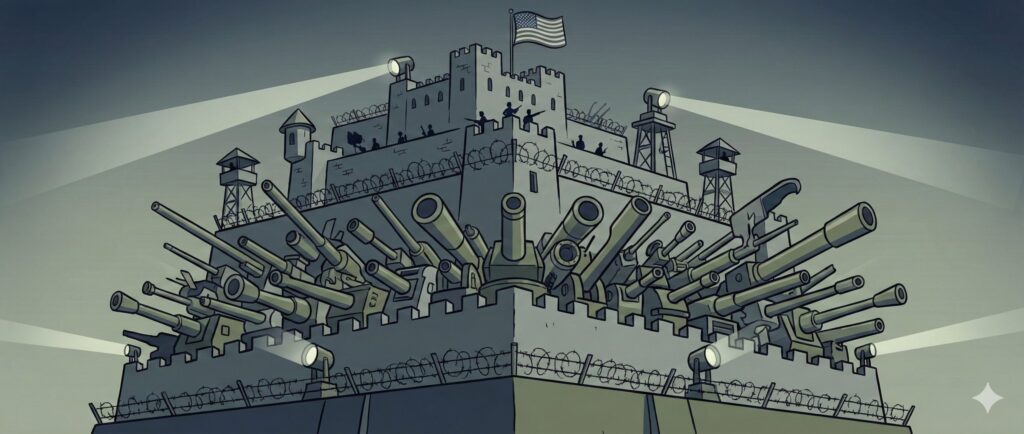
Bloomberg’s report indicates that the national security strategy goes beyond merely tightening regulations; it redefines U.S. policy concerning territorial protection, borders, critical infrastructure, and the national economy. Offensive cyber actions are framed not as instruments of global stability but as essential tools for keeping adversaries at bay, imposing costs, and safeguarding national perimeters. Spearheaded by the Office of the National Cyber Director, this updated strategy is anticipated within the coming weeks and outlines a security doctrine focused on territorial protection, skepticism towards multilateral frameworks, and a besieged fortress mentality.
The proposed document would create clarity regarding the roles of federal agencies and the private sector and incorporate delegated offensive capabilities, particularly targeting ransomware infrastructures and specific foreign state services. This strategy signals a shift from merely providing technical support or responding to incidents towards proactive operations conducted by companies under mandate, protected by specific legal safeguards and ultimately regulated through a presidential decree. The legal framework for these delegated operations is already a topic of debate, with multiple officials acknowledging that current laws do not fully cover such actions.
Enrolling Industry to Enhance Operational Capability
This announcement gains significance when viewed within the broader context of the National Security Strategy released by the U.S. administration in the fall of 2025. The document redefines the relationship between the federal government and the private sector as a pillar of national security, asserting that the ability to “discover, attribute, and respond in real-time to threats” depends on a close integration of network defense and offensive cyber operations. The strategy also expresses a desire for deregulation and simplification of decision-making processes, deemed necessary for swift action. In this framework, the industry transforms from a mere supplier to a force multiplier embedded within the strategic posture. This partial outsourcing of offensive cyber capabilities appears as a method to expand the defense perimeter and enhance state capabilities.
The European Parliament’s research service characterizes this development as symptomatic of a more profound doctrinal shift. The document indicates that the American strategy emphasizes a narrow definition of national interest and places significant focus on domestic security priorities within the hierarchy of external action. It notes a more ideologically charged, concise doctrine that is less committed to multilateral frameworks, departing from previous approaches centered around international cooperation and collective stabilization. This interpretation sheds light on the logic behind delegated offensive cyber strategies, designed not as a means for global regulation, but as instruments of unilateral protection and deterrence.
Acknowledging a Besieged Fortress Mindset
The European Parliament emphasizes that the American strategy operates under a worldview perceived as fundamentally hostile. According to the document, threats are portrayed as “diffuse, constant, and omnipresent,” arising from adversarial states, criminal organizations, or transnational regulatory frameworks viewed as restrictive. This perspective fosters a defensive withdrawal logic, prioritizing the protection of territory, borders, and critical infrastructure above all else.
This approach transforms cybersecurity into a tool of indirect projection. By enabling private firms to execute offensive capabilities, the federal government broadens its operational scope while maintaining political and operational distance. However, the European Parliament cautions against the implications of this delegation, highlighting that it blurs the line between defense and attack and significantly complicates issues related to attribution, accountability, and escalation. The document specifically mentions the risk of collateral damage affecting shared infrastructures and third-party actors, including Europeans.
Another Shock for European Allies
For Europe, the implications extend far beyond the cyber realm. The European Parliament document notes that the American strategy adopts a critical stance towards the European Union, accusing it of contributing to an “erosion of political sovereignty” through regulation and transnational frameworks. This ideological dimension intertwines with an overt transactional logic that conditions cooperation, access to technologies, and industrial advantages on stricter strategic alignment. In the cyber domain, this increases the risk of extraterritoriality, even as numerous European entities rely on American security platforms and services.
The potential involvement of American entities in offensive operations presents immediate governance challenges for European IT leaders. Within private company solutions, the division between detection, protection, and action becomes increasingly difficult to establish, especially when the same providers operate surveillance, incident response, and, in the future, mandated offensive services. As the European Parliament points out, this situation creates a structural asymmetry where American strategic priorities can effectively impose themselves on European organizations without direct oversight or sufficient visibility.
A Strategic Alert Rather than a Technical Debate
The overarching message from the European Parliament is unmistakable. This evolution should not be interpreted simply as an upgrade of American cyber defense capabilities, but as a significant strategic signal. It reveals a security doctrine rooted in distrust, national perimeter protection, and the instrumentalization of industry as an advanced line of defense. The concern transcends the risk of isolated incidents; it is about normalization. Once the premise is accepted that businesses can act on behalf of the state beyond national borders in legal gray areas, the boundary becomes exceedingly porous. Industrial espionage, mass data collection, surveillance of deemed “risky” partners, and indirect pressure on foreign critical infrastructures can all be reclassified as acts of national protection.
European companies now face the imperative of incorporating this factor into their supplier risk management, architectural choices, and technological dependency strategies. The challenge is no longer merely to defend against attacks, but to safeguard against the systemic effects of cyber offensives conducted by allies whose priorities are increasingly unilateral. In essence, the American government appears poised to transfer sovereign prerogatives to private entities that are already deeply embedded within European information systems. These firms have access to security logs, network flows, identities, and collaborative usage. In this respect, the European Parliament is correct: this marks the advent of a permanent state of exception, where security urgency justifies the gradual erosion of safeguards, and where the private sector becomes an unofficial extension of the security apparatus.



