

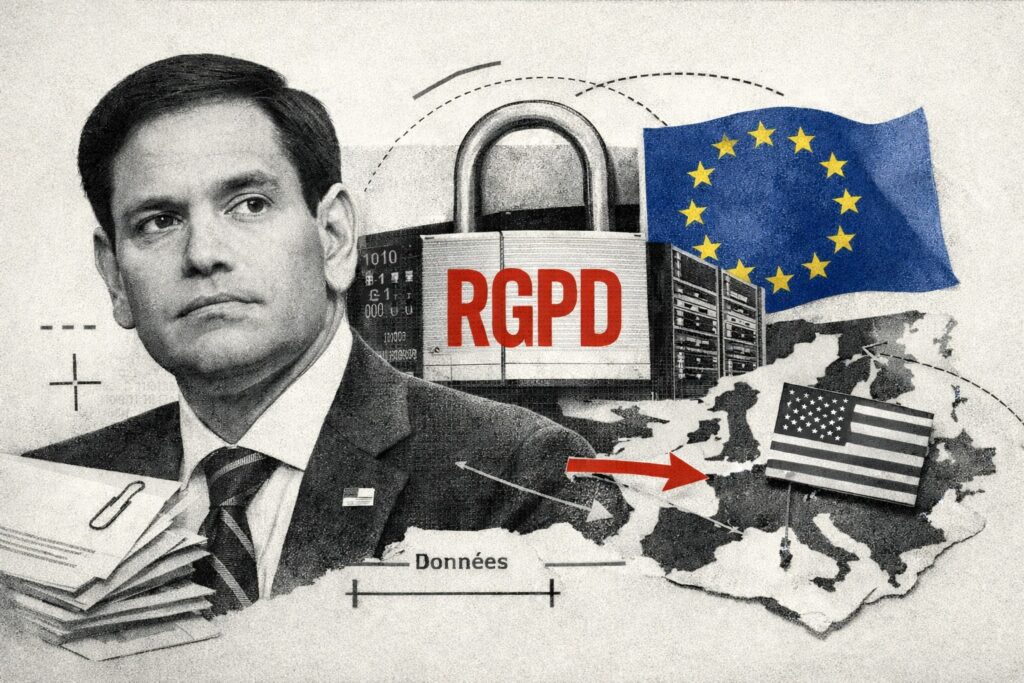
U.S. Secretary of State Orders Diplomats to Push Back Against Foreign Data Regulations
In a notable shift in U.S. digital diplomacy, an internal State Department cable dated February 18 and signed by Secretary of State Marco Rubio instructs American diplomats to actively oppose international legislation regulating how U.S. tech companies manage personal data. This document signifies a new phase in Washington’s international digital strategy, explicitly targeting sovereignty as a key focus of American diplomacy.
Rubio’s cable emerges against the backdrop of escalating tensions between Washington and Brussels over digital regulation. Since 2018, the European Union has constructed a comprehensive regulatory framework—including the GDPR, Digital Services Act, and AI Act—that restricts data flows to third countries and has led to substantial fines against American companies. The dominance of U.S. artificial intelligence firms, which rely heavily on vast amounts of personal data, has intensified European concerns over privacy and surveillance.
The diplomatic cable specifically names the GDPR as an example of regulatory measures that impose restrictions perceived as excessively burdensome on data processing and cross-border flows. This explicit mention is unprecedented in an official State Department document, effectively transforming a European legal framework designed to protect data into a target for formal diplomatic action. For Chief Information Officers (CIOs) and Chief Information Security Officers (CISOs) operating in multinational environments, this evolution implies that GDPR compliance decisions will now occur under increasing U.S. diplomatic pressure, complicating data architecture and processing location choices.
The diplomatic missions have been assigned a dual responsibility. First, they are tasked with monitoring and countering national legislative proposals that promote data sovereignty in their host countries. Secondly, they must actively promote the Global Cross-Border Privacy Rules (CBPR) Forum—an international framework established in 2022 by the U.S., Canada, Mexico, Australia, Japan, and other nations—as an alternative to the prescriptive European regulatory model. The CBPR, based on a voluntary certification system, proposes a drastically different approach to data governance that is less stringent for businesses but offers insufficient user protection compared to GDPR requirements.
A Coordinated Effort Against European Regulation
The Trump administration has articulated its stance using a three-pronged rhetorical strategy. The U.S. government frames data sovereignty laws as potential disruptors of global data flows, increasing costs and cybersecurity risks, limiting AI and cloud services, and augmenting government control in ways that could infringe on civil liberties and enable censorship. This framing positions the free flow of data as fundamental to the advancement of AI, recasting privacy protection and data confidentiality as hindrances to technological innovation and digital security.
The February 18 cable is not an isolated incident; rather, it fits within a broader sequence of U.S. diplomatic interventions aimed at undermining European digital regulatory frameworks. Last year, Rubio had already directed American diplomats to rally opposition against the Digital Services Act. This consistent effort reveals a coherent strategy to weaken the legal underpinnings of European digital regulation even before they could fully impact U.S. businesses.
Moreover, reports suggest Washington is preparing an online portal that would allow users to circumvent content moderation, including restricting content flagged as hate speech or terrorist propaganda. If realized, this initiative would significantly challenge the enforcement mechanisms of the Digital Services Act, which the European Commission primarily oversees.
Technological Decisions Under Diplomatic Pressure
For information technology leaders operating in Europe, Rubio’s cable introduces a new variable into data architecture decisions. Choices regarding processing locations, cloud service provider selection, and structuring cross-border data flows will now be subject to organized American diplomatic pressure.
The promotion of the CBPR Forum as an alternative to GDPR warrants particular attention from CIOs. If this voluntary certification framework gradually establishes itself as a standard in bilateral trade negotiations, it could undermine the extraterritorial reach of the GDPR and diminish European authorities’ leverage over data transfers to the U.S. Decisions made today regarding hosting providers, database locations, and contract structuring are being made within a regulatory landscape whose medium-term stability is explicitly challenged on a diplomatic level.
The European Commission has yet to respond to this development. This lack of immediate reaction contrasts sharply with the urgency highlighted in the American document itself, which mandates diplomats to monitor legislative developments in real-time and to intervene proactively in the legislative process. European client companies will need to navigate data governance in a landscape marked by geopolitical power dynamics, the outcome of which will determine Europe’s regulatory maneuverability in the decade ahead.
The CBPR Forum as a Commercial Alternative to the GDPR
The Global Cross-Border Privacy Rules Forum stands as the cornerstone of U.S. diplomatic efforts. Established in 2022 under U.S. initiative, it includes Canada, Mexico, Australia, Japan, and several other countries in a voluntary certification system for data protection practices. While its positioning as an alternative to GDPR is not new, Rubio’s directive gives it a novel status—transforming it into an official diplomatic tool, with promotion becoming a mission for American representatives worldwide.
The distinction between the two models is fundamental. While the GDPR imposes binding obligations enforceable by independent regulatory authorities equipped with significant penalty powers (with fines against American companies reaching billions of euros since 2018), the CBPR operates on a basis of certification by accredited third parties, lacking comparable sanctions and guarantees of extraterritorial applicability.
The rift between Washington and Brussels over data governance is not new, but as of February 2026, it has crossed a qualitative threshold into systematic and overt diplomatic intervention.



