

Hexatrust and AFNOR Unveil Guide on Outsourced Data Management at the Senate
Hexatrust, the Federation of Trusted Third Parties in the digital space, and AFNOR Normalisation have unveiled a comprehensive guide on outsourced data management targeted at IT and security leaders. This document scrutinizes a frequently overlooked aspect of cloud projects: outsourcing data is tantamount to transferring legal frameworks and responsibilities. Such a shift poses significant risks to trade secrets, operational continuity, and the digital sovereignty of organizations.
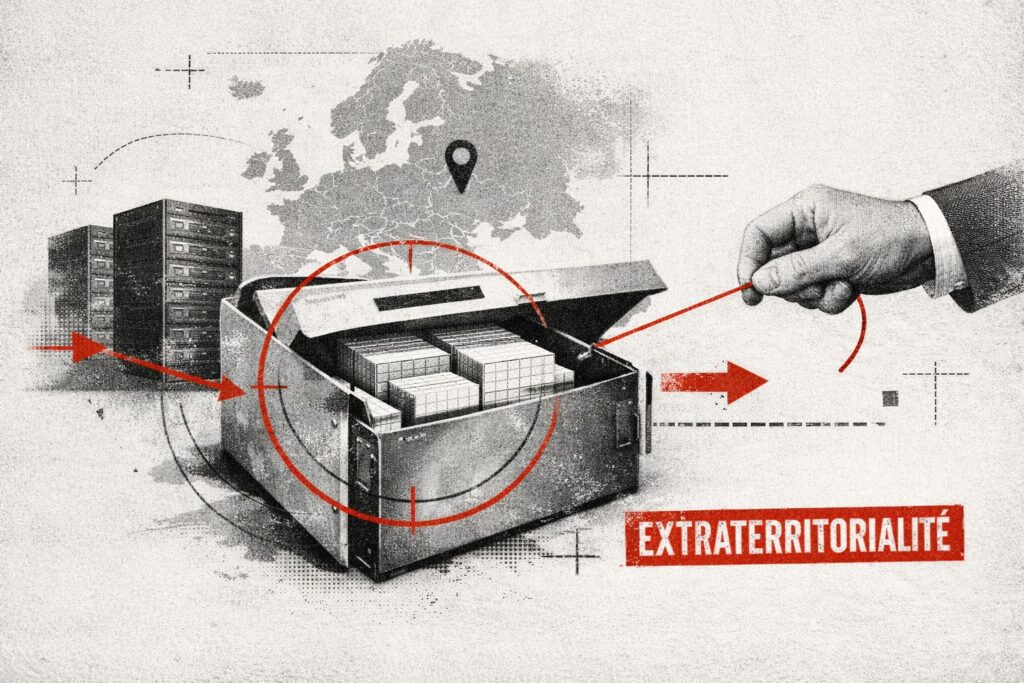
Outsourcing has emerged as a key driver of operational agility, spurred by the widespread adoption of cloud computing and the need to reduce infrastructure costs. However, this convenience comes with its own set of risks. When service providers operate under extraterritorial jurisdictions or utilize a global subcontracting chain, data becomes vulnerable to access by foreign authorities, regardless of its physical location. The distributed nature of modern architectures and replicated processing means that technical geography no longer adequately defines the true exposure of sensitive data.
The guide adopts a largely educational yet direct stance, asserting that the central question is not “where are my data?” but rather “who can legally access it, and under what conditions?” This perspective is particularly relevant for compliance officers and legal departments, as it transforms a simple hosting decision into a strategic choice that impacts the protection of intangible assets, regulatory compliance, and ultimately, competitiveness.
Jurisdiction of the Service Provider Takes Precedence Over Location
The guide illustrates that in a globalized cloud environment, the applicable law primarily hinges on the operating entity and its subcontractors. Even when data is stored within Europe, extraterritorial frameworks such as the Cloud Act or FISA allow foreign authorities to demand access to information held by providers subject to their jurisdiction. These mechanisms often operate without prior notification to the client, resulting in a loss of control over the legal traceability of their data.
This reality reshapes risk assessments for IT and security leaders. Exposure is no longer only about technical security but also involves a mix of architecture, contractual governance, and legal dependence. Therefore, any outsourcing project must proactively include a mapping of applicable laws and subcontracting flows, or risk implicitly agreeing to a loss of sovereignty over strategic data.
Rising Extraterritorial Access Requests
To ground the discussion in real-world implications, the guide references transparency reports from major providers. It highlights that Google reported over 230,000 accounts impacted by FISA requests in 2023, while Microsoft noted more than 28,000 official requests concerning over 52,000 accounts, with a disclosure rate exceeding 64 percent. These figures indicate a regular and increasing reliance on these legal frameworks.
For IT decision-makers, the impact is clear: administrative access to data is neither trivial nor exceptional; it is part of the normalized operations of global platforms. As such, any organization using these services must view this risk as structural rather than an extreme scenario, necessitating a review of classification, encryption, and contracting policies.
Leveraging SecNumCloud and HDS for Legal Risk Management
The guide emphasizes the significant role of French regulatory frameworks. SecNumCloud explicitly includes requirements related to protection from extraterritorial laws, particularly concerning the location of the headquarters, capital ownership, and effective control of the provider. Meanwhile, the updated HDS certification governs remote access to health data from outside the European Economic Area, imposing legal guarantees and client information obligations.
Because these frameworks integrate security, governance, and law, they provide IT leaders with auditable criteria to navigate between service offerings. They convert the abstract notion of sovereignty into measurable contractual and technical requirements, thereby easing the incorporation of extraterritorial risk into architectural committees and procurement processes.
Contracts as the First Line of Defense
The guide outlines a checklist of clauses organizations should seek in their contracts. These include full data restitution in an open format, assistance with data repatriation, certified data deletion from the provider and its subcontractors, transparency on the subcontracting chain, cascade audit rights, and prior notification of changes in control. Each clause addresses a specific mechanism of control loss observed in complex cloud environments.
This approach places contracts at the heart of data governance. As technical dependencies can be difficult to reverse once established, these requirements should be integrated right from the selection phase. Otherwise, organizations risk becoming trapped in an ecosystem where reversibility is a theoretical concept and where legal exposure evolves without effective negotiation leverage.
Beyond technicalities, the guide also embodies an industrial policy dimension. It advocates for data classification prior to outsourcing, prioritizing trusted European solutions, and treating data as a strategic asset. For IT leaders and executives, the stakes extend beyond mere compliance; they must balance immediate operational convenience with the long-term ability to maintain control over their digital assets, particularly in a landscape where artificial intelligence is significantly enhancing the economic value of data.



