

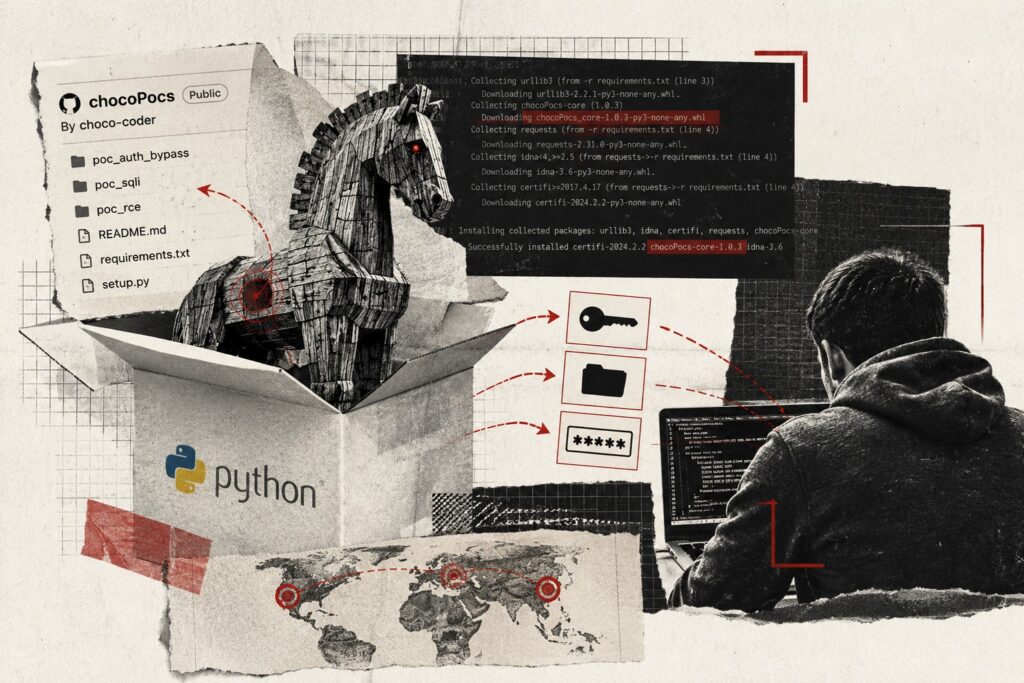
ChocoPoC: A New Trojan Targets Vulnerability Researchers through Fake Proof of Concepts
ChocoPoC is a malicious campaign designed to ensnare vulnerability researchers and penetration testers with counterfeit exploit code repositories. This remote access Trojan embeds itself within the Python dependencies of these proofs of concept, siphoning off credentials, files, and sensitive information from compromised systems. At the time of publishing this analysis, the command infrastructure remained active.
The Vulnerability Intelligence Team at YesWeHack, a French offensive security platform, in collaboration with the Threat Detection & Research team at Sekoia, a French cybersecurity firm, has released a joint analysis of this previously undocumented campaign. Since late 2025, seven GitHub repositories containing these fraudulent proofs of concept—centered around highly scrutinized critical vulnerabilities—have distributed malware known as ChocoPoC. The targets of this campaign are precisely those who work with such code on a daily basis, including vulnerability researchers, penetration testing teams, and scanner developers.
Discovery Through GitHub Notification
The investigation began with a GitHub notification received by YesWeHack at the end of June. An anonymous user proposed two proofs of concept for a critical vulnerability in a Joomla plugin while asking for an associated detection template. A systematic review of the code before execution led researchers to suspect foul play, as the second repository depended on an unknown Python package named “frint,” which was itself reliant on a newly published package called “skytext.” Notably, the account that created the repository had only been active for two weeks.
Infection Hidden in Dependencies, Not Visible Code
The proof of concept code appears harmless at first glance. The malicious payload is concealed within the transitive dependencies installed via pip—a confusion introduced within the repository’s requirements.txt file. The “skytext” package only delivered precompiled native libraries, which were supposed to provide “nice terminal colors.” However, binary analysis revealed an obfuscated loader hidden within. Thus, merely reviewing the repository is no longer sufficient; audits must extend to the packages prompted by the installation.
Time constraints amplify the issue. When a critical vulnerability comes to light, every hour counts in developing a detection module before widespread exploitation occurs, propelling the rush to reuse proofs of concept shared by the community. “Everyone is advised never to execute code from untrusted sources, but urgency can disrupt these good practices,” the researchers from both teams noted.
Triggering Only in the Presence of Specific Files
The compromised library hashes the names of Python modules loaded into memory, executing its malicious payload only if a file named exploit_poc.py exists in the environment. Therefore, running a detonating test in an isolated sandbox triggers nothing, which explains the total lack of detection on VirusTotal at the time of analysis. The malware incorporates anti-debugging routines and tampers with file timestamps to obfuscate investigations.
This persistence mechanism hijacks a legitimate component of the Python ecosystem. The loader deposits a .pth file and a trojanized _distutils_hack package into the packages directory, ensuring the payload reactivates each time an interpreter starts. Consequently, the system remains compromised, regardless of the original proof of concept.
Mapbox Used as a Dead Drop
The downloader resolves the address of the mapping service Mapbox through DNS queries encrypted within HTTPS traffic, then queries a dataset where the attacker has deposited their encoded payload. The TLS handshake and certificate match those of the legitimate service, allowing the command channel to blend seamlessly into standard API usage and evade DNS blocks as well as detection tools scrutinizing the system.
Once installed, ChocoPoC exfiltrates passwords, cookies, and browsing histories from Chrome, Brave, Edge, and Firefox, gathers terminal histories, text files, and local databases, and executes arbitrary commands on the machine. Large exfiltrated data transfers are directed to a dedicated server controlled by the attacker.
Two Waves of Attacks, One Actor, Timed with Trending Vulnerabilities
The seven identified repositories targeted high-profile vulnerabilities in FortiWeb, React2Shell, PAN-OS, Ivanti Sentry, Check Point VPN, and Joomla. Two waves of attacks occurred in 2025 and 2026, utilizing a rotating set of GitHub, PyPI, and Mapbox accounts to evade bans. Researchers attribute the entire operation to a single actor based on technical identifiers that were reused across waves, noting that publishing accounts relied on compromised email addresses found in data breaches.
The “skytext” package has amassed approximately 2,400 downloads, predominantly on Linux. Download spikes correlate with the disclosure of vulnerabilities and their addition to CISA’s catalog of exploited vulnerabilities, peak occurring in early May with the “Linux Copy Fail” vulnerability. Researchers perceive this as evidence of unnoticed prior infection waves, further indicating the industrialization of cybercrime.
For CISOs and heads of offensive teams, this campaign shifts the focus of vigilance. Validation must encompass transitive dependencies before any installation takes place, running proofs of concept should be confined to disposable environments devoid of sensitive data, and monitoring outbound traffic should include legitimate SaaS APIs. With the infrastructure still active, YesWeHack and Sekoia advise against executing code from the identified repositories or installing the implicated packages.



