

Almond Launches Comprehensive Resilience Operation Center to Enhance Cyber Resilience
Almond is stepping up its game in cyber monitoring, threat analysis, and incident response with the launch of its new Resilience Operation Center (ROC). This integrated offering embodies a “resilience by design” approach, establishing itself as a vital component in the governance of continuity for critical information systems.
In today’s world, resilience is no longer an optional feature of security systems but a structural necessity. Organizations facing demands for continuity, compliance, and agility must possess the ability to withstand digital shocks, restore critical functions, and rebuild safer environments. In this context, Almond announced the establishment of its ROC on January 6, 2026, aiming to provide a unified framework for operational cyber resilience.
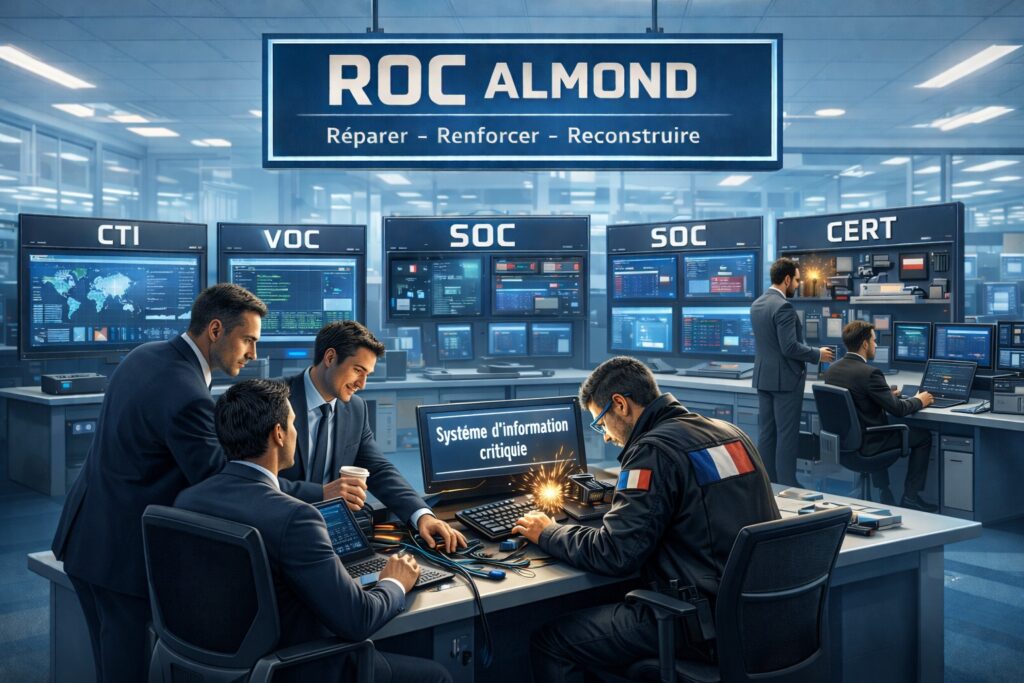
The ROC is built around four interlinked technical components: a Threat Intelligence Center (CTI), a Vulnerability Management Center (VOC), a 24/7 Security Operations Center (SOC), and an Emergency Response Team (CERT). This coordinated structure ensures a comprehensive resilience loop encompassing anticipation, detection, response, and recovery, enabling the seamless integration of cyber risk management with business imperatives.
Breaking Down Silos for Better Recovery
The ROC addresses a threefold evolution of expectations within the cybersecurity landscape. First, it acknowledges that invulnerability is a myth; true strength lies in an organization’s capacity to absorb attacks, protect vital functions, and coordinate a swift return to normalcy. Second, there is a pressing need for convergence across security functions, IT operations, and business responsibilities. Lastly, heightened compliance demands, especially in critical sectors governed by regulations like NIS2 and DORA, necessitate a robust operational resilience framework.
Operationally, ROC teams handle the entire continuum of response: identifying exploitable vulnerabilities, continuously hardening environments, investigating post-attack incidents, removing persistent threats, and redesigning infrastructures guided by “security by design” principles. The goal is not merely to restore systems to their former state but to create a more robust architecture that incorporates lessons learned from prior attacks. This process is enhanced through orchestration tools, automation, and unified governance models.
Continuous Mobilization and Incident Response Capabilities
With over 120 specialized personnel, the ROC can be mobilized both proactively and during major incidents. Equipped with advanced tools for behavioral analysis, event correlation, automated vulnerability management, enriched cyber intelligence, and in-depth digital investigations, the ROC ensures a smooth transition between strategic monitoring, daily operations, and crisis management, operating continuously around the clock.
The leadership of this innovative structure falls to Alexandre Faraino and Marine Pelé, seasoned Almond executives who have previously overseen SOC, CERT, CTI, and managed cloud services. Their mission is to ensure coherent responses, foster innovation, and enhance technical effectiveness. The ROC’s organizational model promotes functional horizontality and aligns teams around measurable resilience indicators.
Meeting Regulatory Demands for Traceable Resilience
The establishment of the ROC is also a response to heightened regulatory expectations in cybersecurity. New European directives require not only prompt intervention capabilities but also traceability of actions, risk scenario assessments, and demonstrable recovery capabilities. Now, resilience plans must be documented, tested, and aligned with organizations’ legal and contractual obligations. Almond addresses these needs with an auditable approach based on decision-making dashboards and certifiable processes.
This framework particularly benefits organizations subject to sector-specific regulations (such as finance, healthcare, energy, and critical infrastructure) along with major enterprises engaged in certification or extraterritorial compliance efforts. In this light, Almond’s ROC serves as both a risk reduction lever and a strategic tool for fostering digital trust and long-term competitiveness.
Towards a European Model of Integrated Cyber Resilience
With its structured approach and promises, Almond’s ROC aligns with market demands for sovereignty and functional integration. Centralizing its SOC, VOC, CTI, and CERT capabilities allows for a cohesive response tailored to European requirements for digital trust, all underpinned by strong local engagement. Almond emphasizes its sovereign stance, operating with teams in France and Switzerland, alongside international service centers to ensure continuous coverage.
This strategic positioning resonates with the transformation of the European cyber ecosystem: increasing regulatory obligations, the emergence of shared frameworks (such as EUCS and EUCC), the growing importance of managed security services, and the quest for partners capable of supporting the entire resilience cycle. Through this organizational evolution, Almond aims to establish itself as a leading player in integrated cyber resilience across Europe.



