
Anatomy of a Microsoft SharePoint Server Vulnerability Exploited to Deploy the Warlock Ransomware
A critical vulnerability in Microsoft SharePoint Server, which was patched in May, has been exploited for weeks as an entry […]
A critical vulnerability in Microsoft SharePoint Server, which was patched in May, has been exploited for weeks as an entry […]
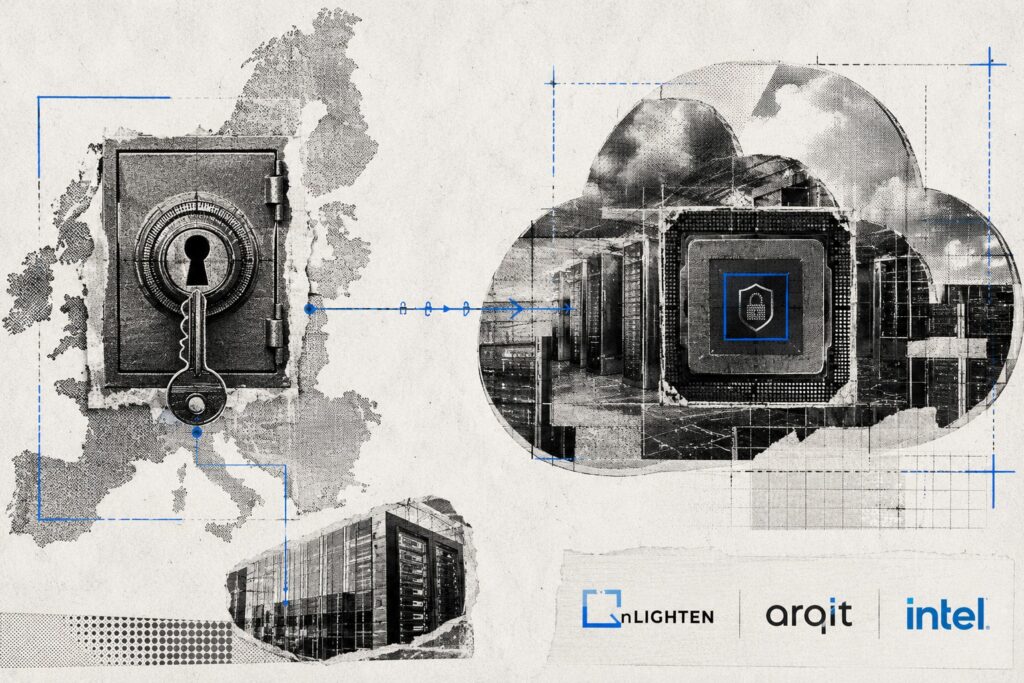
nLighten and Arqit Expand Cloud Sovereignty with Innovative Proof of Concept nLighten and Arqit have co-developed a proof of concept
The CERT-FR has reported a significant vulnerability, Januscape (CVE-2026-53359), which allows an escape from a virtual machine to the host
Barracuda Networks has acquired Evo Security, a U.S.-based provider of Identity and Access Management (IAM) solutions tailored for Managed Service
European Commission Unveils Cybersecurity and AI Action Plan On July 7, the European Commission unveiled a comprehensive action plan for
The European Parliament will vote on July 9th regarding the extension of the controversial Chat Control scheme, a regulation that
Hexatrust, the French association representing stakeholders in cybersecurity, trusted cloud, and digital workplaces, held its annual general meeting on July
Sysdig Unveils JADEPUFFER: Investigating the First Full-Language Model-Driven Ransomware Operation Sysdig’s research lab has uncovered what it describes as the
The National Cybersecurity Agency of France (ANSSI), the Prudential Supervision and Resolution Authority (ACPR), and the Bank of France have
Citrix has patched six vulnerabilities in its NetScaler ADC and NetScaler Gateway appliances, including a critical memory leak flaw that